When Logos Become Security Credentials: How Trademark Law Now Shapes Email Authentication
Email security is no longer just a technical discipline. It is becoming a legal one.
For decades, email authentication was purely technical: SPF, DKIM, DMARC.
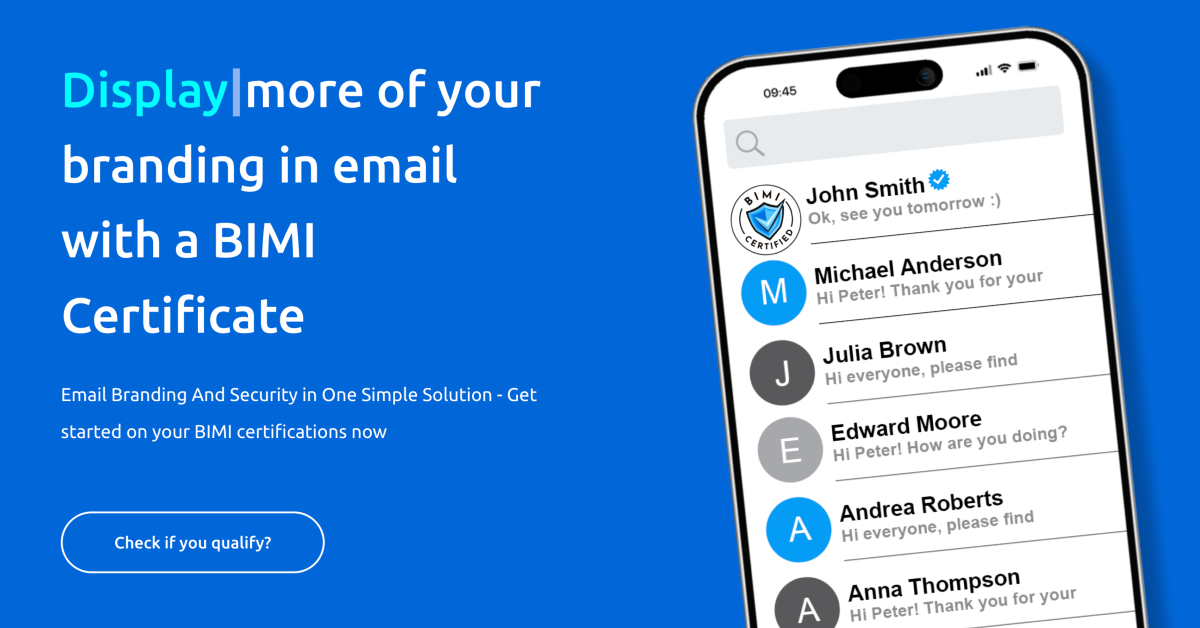
No lawyers. No trademarks. No certificates. Then BIMI arrived.
And with it came the VMC – a certificate that requires:
- a registered trademark,
- in a recognised jurisdiction,
- matching the exact logo used in email.
Suddenly, email security teams found themselves asking questions such as:
- “Is our logo actually registered?”
- “In which jurisdiction?”
- “Does the trademark match the logo we use in marketing?”
- “When does it expire?”
- “Can we even get a VMC with this?”
Most companies do not know the answers.
And that is the bottleneck.
The legal system moves slowly – but email threats move fast
A DMARC policy can be deployed in days. A BIMI record can be published in minutes.
But a trademark registration?
- 3–6 months if everything goes well,
- longer if objections arise,
- much longer if the logo needs updating.
This mismatch creates a strange reality: your domain can be protected today, but your verified brand identity in the inbox may have to wait – until the trademark office has made its decision.
VMC forces brands to tidy up their identity
Most companies have:
- multiple logo versions,
- outdated trademark filings,
- inconsistent brand usage,
- expired registrations,
- logos registered only locally, not internationally.
VMC demands discipline. To be verified, a brand must have:
- one official logo,
- registered in a recognised jurisdiction,
- matching the exact artwork used in email,
- with a valid, active registration.
For many organisations, this is the first time marketing, legal and security teams have worked together on a single project – and it shows.
The trademark bottleneck is actually a good thing
It sounds like a hurdle – and it is – but it is also a powerful filter. Brands that:
- protect their identity,
- maintain their trademarks,
- invest in authenticity,
- take security seriously
…are better prepared for the verified checkmark. This raises the bar for the entire ecosystem.
The future: trademark law becomes part of cybersecurity strategy
Brand protection will no longer be only a legal task – it will also be part of cybersecurity. Companies will need to:
- register trademarks earlier,
- maintain them proactively,
- align brand identity with legal filings,
- treat trademark expiry as a security risk,
- integrate legal timelines into security roadmaps.
Organisations that understand this will move faster. Others may wait months for a verified logo – while attackers move in milliseconds.
Your logo is now part of your security perimeter
A brand’s visual identity is now directly tied to its email security posture. Your logo is no longer just a marketing asset – it is also a security credential. Readiness for verification in the inbox therefore depends not only on your IT team, but also on the status of your trademark (for a VMC) or on evidence of logo use (for a CMC).